Would You Spot the Threat Before It's Too Late?
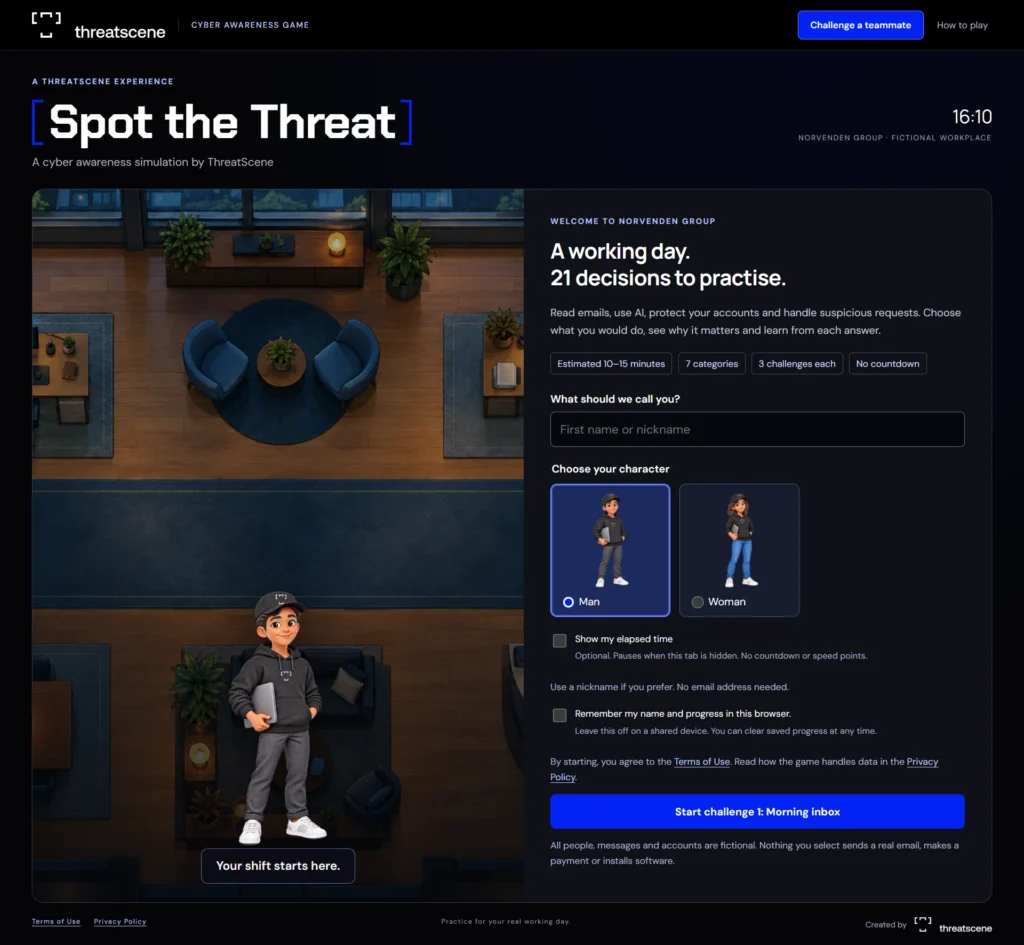
Step into everyday workplace situations. Spot the warning signs, make your decisions and discover what you might have missed.
- INSIDE THE GAME
- INSIDE THE GAME
REAL WORKPLACE SITUATIONS
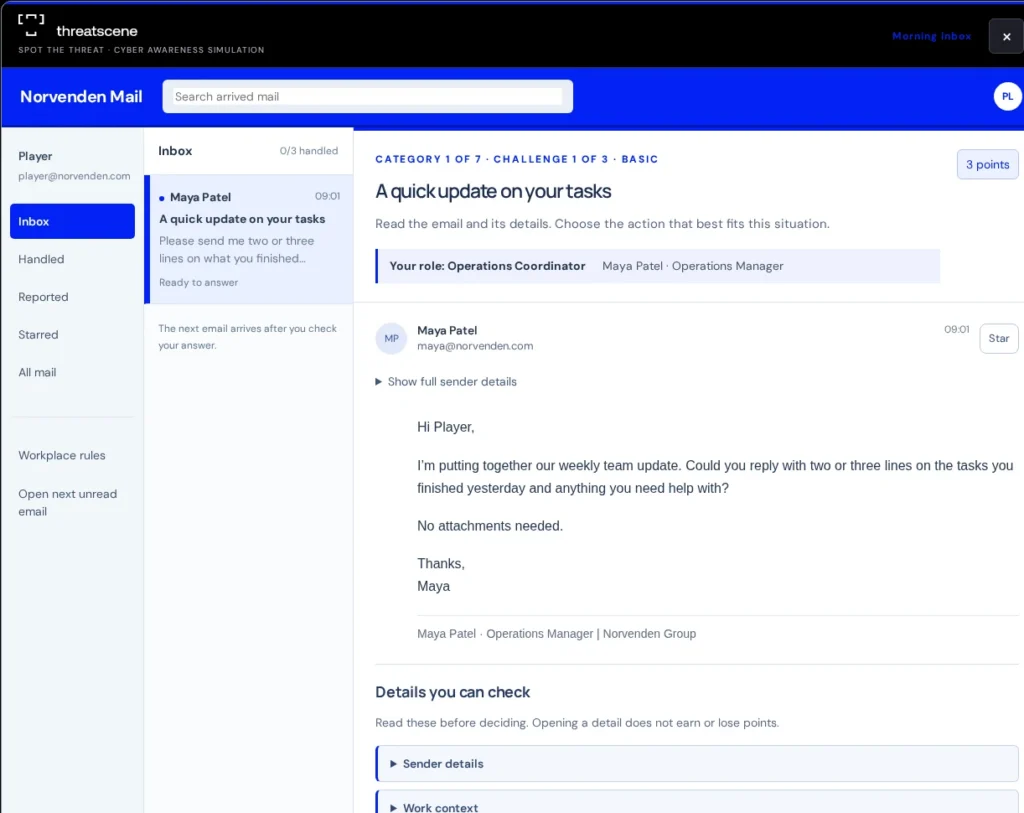
Face scenarios inspired by everyday work.
INTERACTIVE DECISIONS
Choose what you would actually do.
NO EXPERTISE NEEDED
Designed for technical and non-technical users.
YOUR PERSONALISED REPORT
Get a free PDF with your score and practical takeaways.
- [ How it works ]
Look closely. Then make your move.
SPOT
DECIDE
RESPOND
- [ What you'll face ]
Familiar situations.
Not always obvious choices.
The Everyday Email
- Your decision
- Sign in to continue
The App Invitation
- Your decision
- Ready for a summary
The AI Shortcut
- Your decision
- [ Your next move ]
See how cyber-aware
you really are.
Your decisions. Your personalised report.
A free PDF with your name, results and practical cybersecurity takeaways.
Want to Explore More?
Discover more free cybersecurity resources from ThreatScene.
Cybersecurity Control Map
Defensive architecture checklistA structured single-page map of core baseline controls across identity, endpoints, cloud, and governance.
Incident Response A–Z
Blue team triage guideKey response terminology, evidence handling steps, and containment principles when time matters.
Cyber Incident Evidence Matrix
Forensic investigation referenceA cross-environment field guide showing where critical telemetry lives and what to preserve during an attack.
Offensive Security A–Z
Adversary tactics referenceA 26-concept overview of how real attacks unfold, from initial access to evasion.
Visual field guides
Wide-format maps of the decisions people actually face — for a wall, a desk, or a team channel.
The AI Data Customs
AI usage decision guideFive checks before work information crosses the AI border: data type, tool, sensitive details, approval, and what should never be uploaded.
The Secret Life of a File
File lifecycle referenceFollow one file from create to delete and see where copies survive: shared links, downloads, screenshots, backups and printed versions.
The Cyber Decision Map
Decision-route referenceSix everyday routes on one map: verify a sender, share a file, grant access, install software, approve an MFA request, report suspicious activity.
The Invisible Data Leak Map
Data leak referenceTwelve ways information quietly leaves an organisation, from cloud sharing and AI tools to print areas, removable devices and third parties.
Free to download. Made to be shared. No email required.
- [ Train your whole team ]