Cyber Resilience Starts Before the Incident
ThreatScene is a cybersecurity company helping organisations prepare for, withstand and recover from cyber threats across critical and complex environments. We connect offensive security, cyber defence, incident response, consulting and training to strengthen resilience before threats become disruption.
- 24/7
- Incident Response Availability
- 4 Connected Capabilities
- Offensive, Defensive, Consulting and Training
- Critical Sectors
- Maritime, Infrastructure, Finance and Enterprise
Built for the Threats That Disrupt the Real World
See how ThreatScene brings offensive security, cyber defence, consulting and training together to protect critical industries where downtime has real consequences.
What the Film Explores
- Critical industries cannot afford prolonged disruption
- Unit 13 and Unit 31 operate as one connected system
- Offensive, Defensive, Consulting and Training strengthen resilience together
- Maritime
- Finance
- OT and Energy
- Healthcare
- Government
“The question is not only whether an organisation will be targeted. It is whether it is prepared when that happens.”
The Threat Landscape Has Changed. Cybersecurity Must Change With It.
Cybersecurity can no longer be treated as a collection of isolated tools and compliance tasks. Modern incidents affect operations, revenue, reputation and trust. Organisations need preparation, context and tested response capabilities before an attack begins.
From Traditional Security to Cyber Resilience
Readiness Over Reaction
Cyber resilience is built before an incident through preparation, visibility, tested response plans and clear responsibilities.
An incident response retainer reduces time lost to procurement, access approvals and responsibility gaps during a live incident.
Context Over Checklists
Security decisions must reflect the organisation’s actual operations, risk exposure, regulatory duties and business priorities.
The same vulnerability can create very different consequences in a corporate office, production environment or connected vessel.
Connected Resilience Over Isolated Controls
Technology alone cannot contain disruption. Organisations need connected expertise across prevention, detection, response, governance and people.
ThreatScene combines offensive security, cyber defence, consulting and training instead of treating each capability as an isolated service.
One Partner Across the Cybersecurity Lifecycle
ThreatScene connects four specialist capabilities to help organisations identify exposure, strengthen defence, manage risk and prepare their people.
Offensive Security
Identify exposure before attackers exploit it.
- Penetration Testing
- Red Teaming
- Vulnerability Assessment
Defensive Security
Detect, investigate, contain and recover from real threats.
- Digital Forensics and Incident Response
- Incident Response Retainer
- Threat Intelligence
- Compromise Assessment
Consulting
Connect cybersecurity with business risk, regulation and operations.
- Cybersecurity Consulting
- GRC Consulting
- Configuration Review
- ThreatScene M.A.R.I.N.E.
Training
Prepare people and processes for real-world incidents.
- Security Awareness
- Phishing Simulation
- Ransomware Simulation
Identify exposure before attackers exploit it.
- Penetration Testing
- Red Teaming
- Vulnerability Assessment
Detect, investigate, contain and recover from real threats.
- Digital Forensics and Incident Response
- Incident Response Retainer
- Threat Intelligence
- Compromise Assessment
Connect cybersecurity with business risk, regulation and operations.
- Cybersecurity Consulting
- GRC Consulting
- Configuration Review
- ThreatScene M.A.R.I.N.E.
Prepare people and processes for real-world incidents.
- Security Awareness
- Phishing Simulation
- Ransomware Simulation
Offensive and Defensive Expertise, Working as One
ThreatScene's specialised operational units connect adversary thinking with real-world defence. Unit 13 tests how organisations can be breached. Unit 31 investigates, contains and responds when threats become real.
Unit 13
Unlucky for Some.
Our red team specialists simulate real adversaries, expose weaknesses and help organisations strengthen their defences before attackers strike.
Explore Unit 13Unit 31
Order out of Chaos.
Our defensive specialists investigate incidents, uncover attacker activity, contain threats and help organisations restore control.
Explore Unit 31Cybersecurity for Environments Where Disruption Has Real Consequences
ThreatScene supports organisations operating across regulated, interconnected and operationally demanding sectors. Our approach reflects each environment's specific risks, systems and resilience requirements.
Maritime
Protecting connected vessels, shore operations and fleet-wide systems against cyber disruption.
- Vessel and shore-side resilience
- Maritime incident response
- Regulatory and operational readiness
Government and Defence
Supporting sensitive environments where cybersecurity, operational continuity and national interests intersect.
- Secure critical systems
- Incident readiness
- Adversary-focused testing
Energy and Critical Infrastructure
Strengthening resilience across IT and OT environments where downtime can affect essential services.
- IT and OT security
- Operational continuity
- Incident investigation and containment
Finance and Fintech
Protecting financial systems, customer data and high-volume digital transactions from evolving threats.
- Digital service resilience
- Regulatory compliance
- Threat detection and response
Insurance
Helping insurers manage cyber exposure, regulatory requirements and incident-related business risk.
- Cyber-risk assessment
- Data protection
- Incident preparedness
Healthcare
Protecting connected medical systems, patient information and essential healthcare operations.
- Patient data protection
- Connected-device security
- Operational availability
Manufacturing
Securing connected production environments where cyber incidents can disrupt safety, output and supply chains.
- IT and OT visibility
- Production continuity
- Vulnerability and incident management
Enterprise Environments
Helping complex organisations reduce exposure across users, infrastructure, cloud services and third parties.
- Enterprise attack-surface management
- Incident response
- Governance and security maturity
Protecting connected vessels, shore operations and fleet-wide systems against cyber disruption.
- Vessel and shore-side resilience
- Maritime incident response
- Regulatory and operational readiness
Supporting sensitive environments where cybersecurity, operational continuity and national interests intersect.
- Secure critical systems
- Incident readiness
- Adversary-focused testing
Strengthening resilience across IT and OT environments where downtime can affect essential services.
- IT and OT security
- Operational continuity
- Incident investigation and containment
Protecting financial systems, customer data and high-volume digital transactions from evolving threats.
- Digital service resilience
- Regulatory compliance
- Threat detection and response
Helping insurers manage cyber exposure, regulatory requirements and incident-related business risk.
- Cyber-risk assessment
- Data protection
- Incident preparedness
Protecting connected medical systems, patient information and essential healthcare operations.
- Patient data protection
- Connected-device security
- Operational availability
Securing connected production environments where cyber incidents can disrupt safety, output and supply chains.
- IT and OT visibility
- Production continuity
- Vulnerability and incident management
Helping complex organisations reduce exposure across users, infrastructure, cloud services and third parties.
- Enterprise attack-surface management
- Incident response
- Governance and security maturity
Credibility Built Through Validation, Operations and Expertise
Bureau Veritas-Endorsed Maritime Cybersecurity
The M.A.R.I.N.E. Cyber Security Framework is endorsed by Bureau Veritas Marine & Offshore.
Incident Response When Disruption Cannot Wait
Round-the-clock support to investigate, contain and recover.
Unit
13Unit
31Two Elite Units. One System.
Unit 13 brings adversary thinking. Unit 31 brings investigation, containment and recovery.
Explore Units 1331Research That Advances the Field
Real-world offensive and defensive findings turned into technical research.
Two Gold Awards. Two Areas That Define Our Work.
Recognition for work across two areas central to ThreatScene’s expertise: maritime cybersecurity and incident response.
Gold Award 2026
Maritime Cybersecurity
Project — ThreatScene M.A.R.I.N.E.
Recognition of ThreatScene’s maritime cybersecurity framework, developed around the operational and regulatory realities of the shipping industry.
Gold Award 2026
Incident Response & Vulnerability Management
Project — Deadlock
Recognition of ThreatScene’s work responding to a real-world cyber incident through investigation, containment and restoration of critical operations.
Helping Organisations Remain Prepared, Operational and Resilient
ThreatScene exists to help organisations manage cyber risk before, during and after an incident. We combine technical expertise, operational understanding and clear guidance to help clients make better security decisions and respond effectively when conditions become complex.
Prepared
Exposure identified, defences tested and people rehearsed before an incident begins.
Operational
Threats detected, investigated and contained while operations keep running.
Resilient
Recovery, root-cause understanding and improvements that reduce future risk.
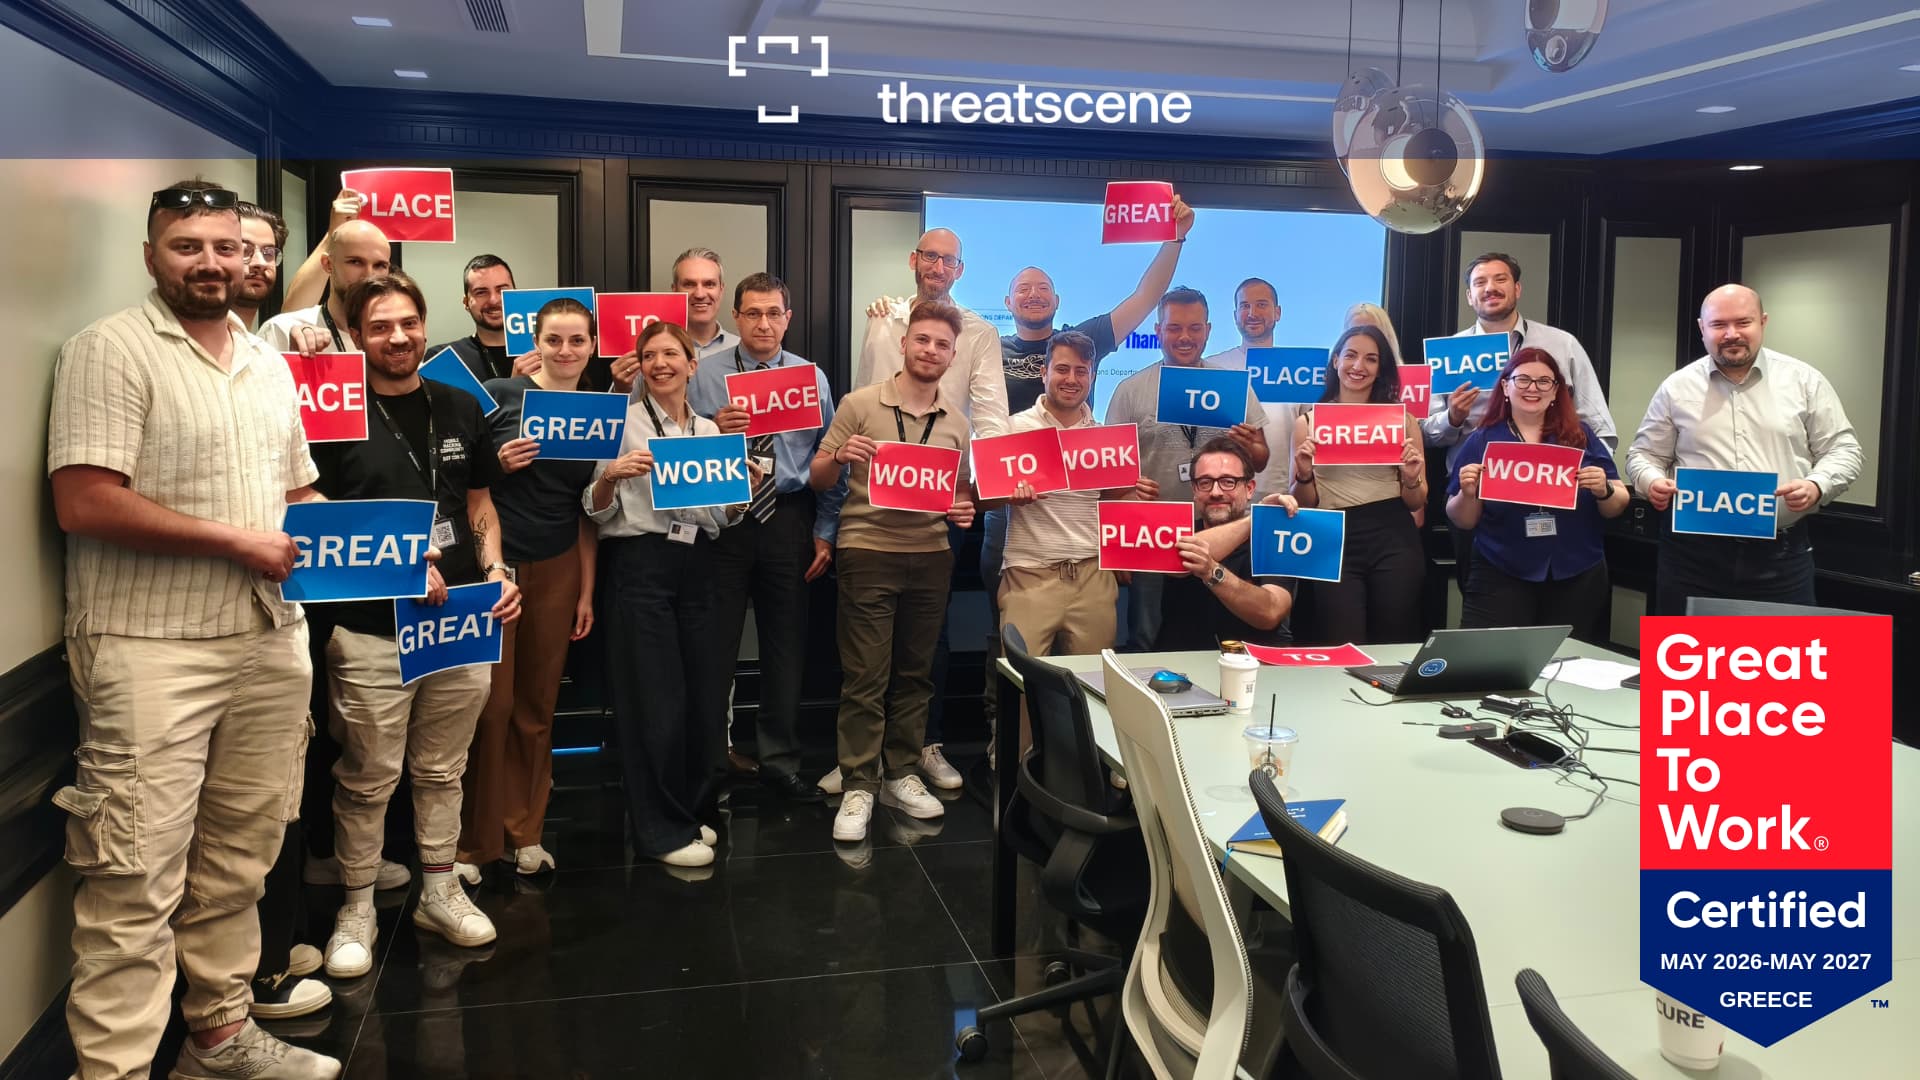
Strong Cybersecurity Starts With Strong Teams
ThreatScene brings together specialists across offensive security, incident response, digital forensics, threat intelligence, GRC and cybersecurity consulting. Our culture is built around collaboration, continuous development and technical excellence.
Great Place to Work Certified & Best Workplaces for Young Professionals
Independent certifications based on team feedback, recognising a workplace built on trust, growth and collaboration.
- Offensive Security
- Incident Response
- Digital Forensics
- Threat Intelligence
- GRC
- Cybersecurity Consulting
- Security Engineering
- Training & Awareness
Go Deeper Into Our Expertise
Elite Units 1331
Meet the offensive and defensive teams behind ThreatScene's specialist capabilities.
Maritime Cybersecurity
Explore M.A.R.I.N.E. and NAVESTIGO, built around the operational realities of maritime environments.
Insights and Research
Read practical cybersecurity analysis from ThreatScene specialists.
Careers at ThreatScene
Discover the roles, culture and opportunities behind our growing team.
Two Paths Into ThreatScene
Strengthen Your Cyber Resilience
Speak with our specialists about your risks, priorities and incident readiness.
Book a ConsultationBuild Your Career at ThreatScene
Explore opportunities to work across complex cybersecurity challenges and critical environments.
Explore Careers